 What's trending, explained.
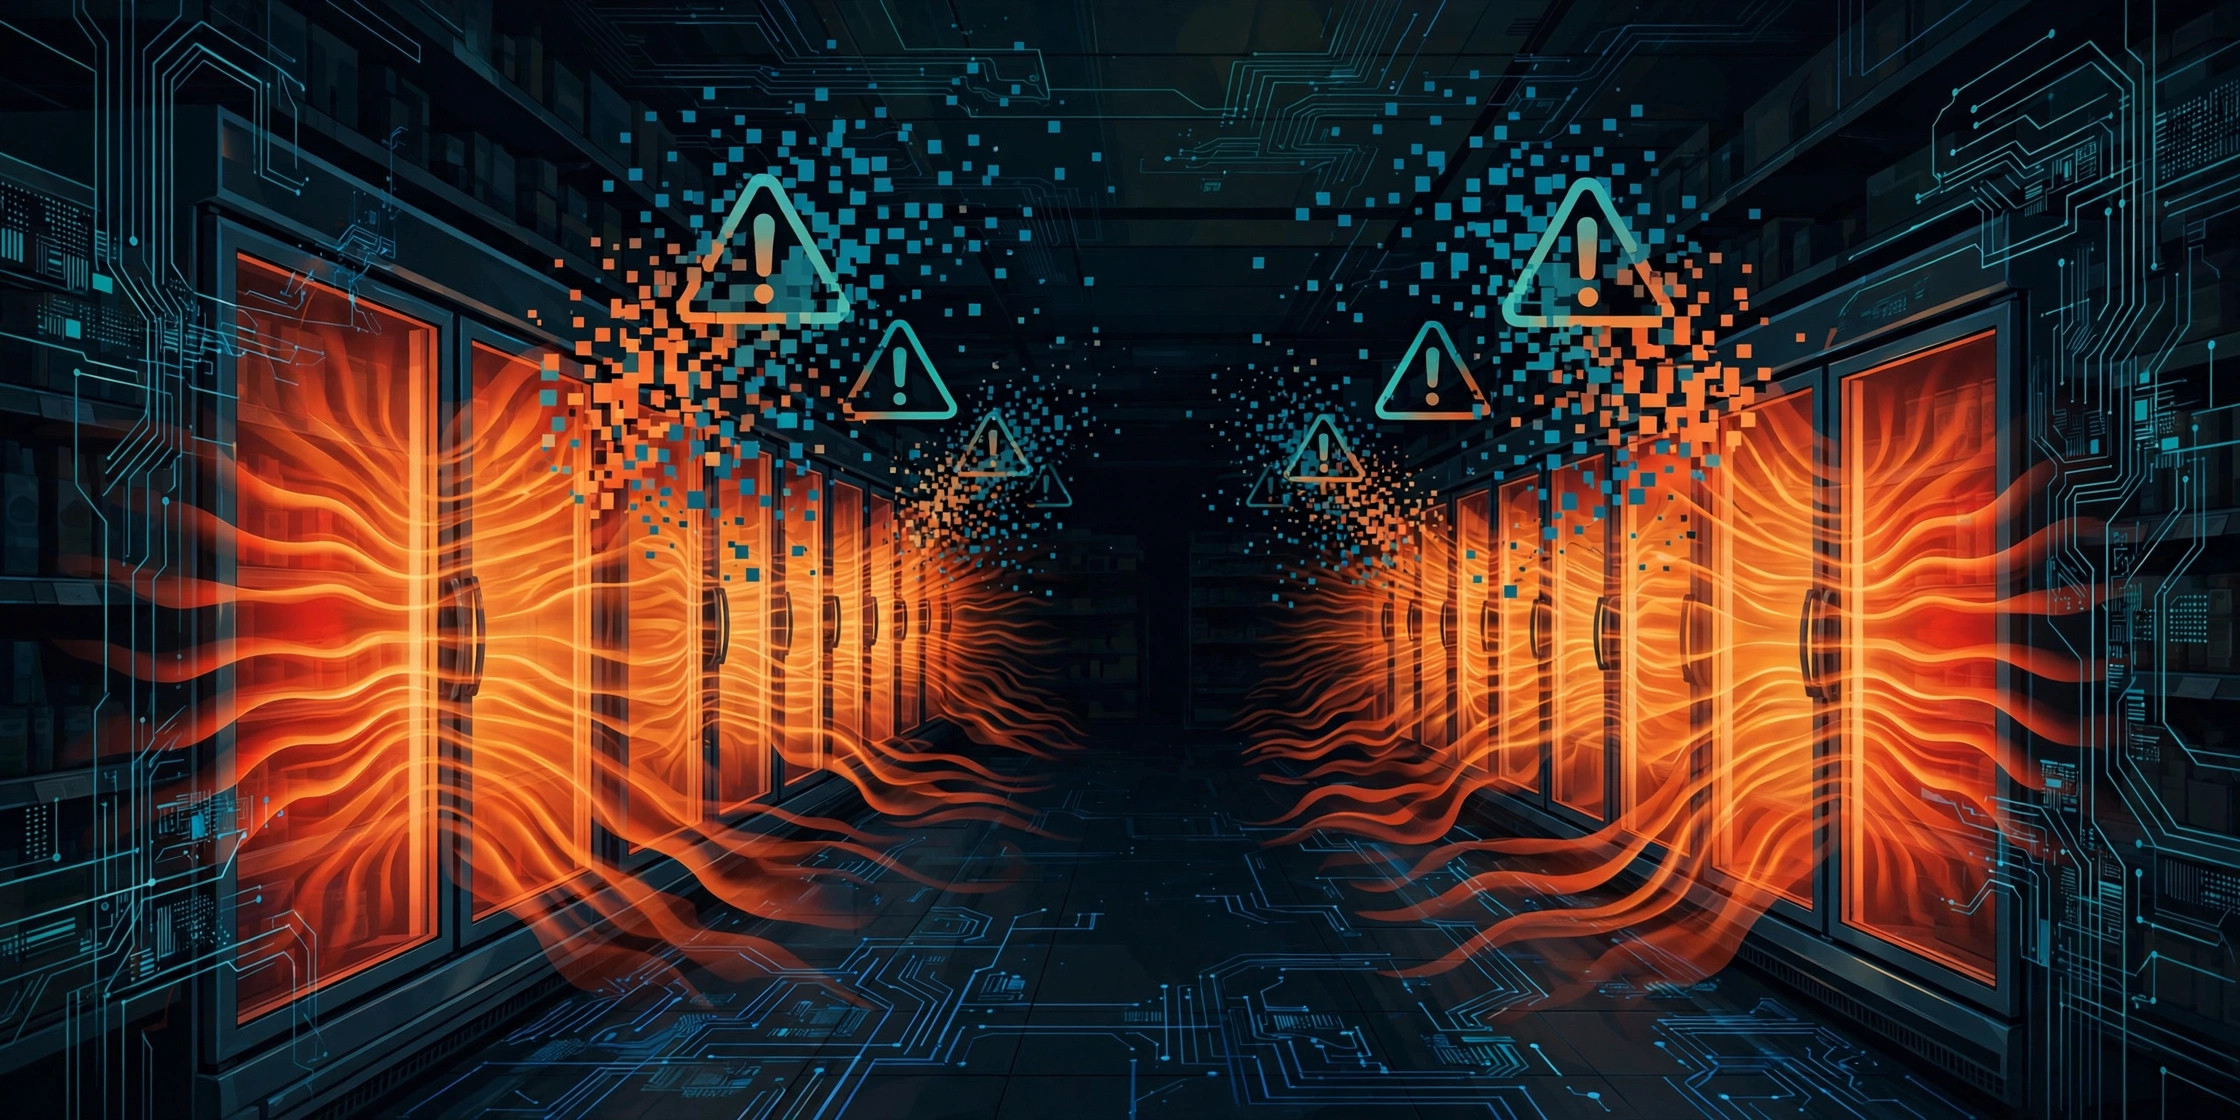
Overnight between October 11 and 12, 2026, hackers forced the temperatures of supermarket refrigerators across France up to 50 degrees Celsius (122 degrees Fahrenheit), causing fires and major food losses at several hundred stores. The Paris prosecutor's office described it as a large-scale cyberattack affecting connected refrigeration equipment at several major food retailers, with reported damage including food losses and fires.
The scale became clear as retailers reported in. Les Mousquetaires, which owns Intermarché, said around 150 of its stores had been hit, with fridges heated to 50 degrees for about six hours; it discarded all the affected food to avoid sanitary risks. Coopérative U confirmed that dozens of its Super U and Hyper U stores were hit, and its CEO Dominique Schelcher called the attack unprecedented in its targeting of equipment essential to the food supply. Carrefour said 80 of its supermarkets were affected, while noting the vast majority of its roughly 6,000 stores were untouched. Other major chains, including E.Leclerc, Monoprix, and Auchan, did not immediately confirm whether they had been affected.
The incident appeared to cross borders. Dutch operator Ahold Delhaize, which runs the Netherlands' largest supermarket chain Albert Heijn and has substantial operations in the United States, said it was also dealing with a security issue in its network and had taken several systems offline to protect them. Its stores stayed open, but its online app and delivery system went down and electronic price tags displayed incorrect information.
France's response was swift. Prime Minister Sébastien Lecornu instructed the national cybersecurity agency ANSSI to investigate, and the government said it was coordinating with European counterparts because other countries could also be affected. The Paris prosecutor's office opened a formal investigation assigned to the national anti-cybercrime office.
This was not a data breach or a website defacement — it was an attack on operational technology with physical consequences. Instead of targeting payment terminals or customer-facing systems, the attackers went after the control systems that regulate refrigerators, freezers, display cabinets, and cold rooms. Technical accounts suggest they hijacked a protective defrost function, forcing a continuous defrost cycle with a temperature setpoint of roughly 50 degrees, effectively turning refrigerated units into heaters for hours. The affected systems appear to be industrial control units made by Danfoss, widely deployed across French retail chains — which would explain how one intrusion could reach hundreds of stores at different companies simultaneously.
That pattern is what alarms cybersecurity officials. It mirrors the logic of the attacks on industrial control systems that experts have warned about for years: a single vendor's equipment, networked for remote management, becomes a single point of failure across an entire sector. France's food retail supply chain discovered this in the most literal way — warm food, spoiled stock, and in some stores, fires.
The cross-border dimension raises the stakes further. The Ahold Delhaize incident, happening at the same time, suggests either the same attackers, copycats, or a shared vulnerability being exploited opportunistically. France coordinating with European counterparts signals that investigators are treating this as a potentially continental campaign, not an isolated incident. Attribution is unknown: no group has claimed responsibility, and prosecutors have said nothing about who is behind it.
The ANSSI investigation is now the center of the story. Investigators will be reconstructing how the attackers got in — whether through the refrigeration management networks, a vendor's remote-access system, or compromised credentials — and identifying every company at risk. France said specialists are mapping potentially exposed firms to alert them, which means more disclosures may follow.
Watch for four developments. First, attribution and motive: prosecutors have not said who did this, and the question of whether it was a criminal ransom operation, a state-backed probe of infrastructure, or something else will shape the response. Second, the Danfoss angle: if a vendor vulnerability was the entry point, expect a patch-and-warning cycle affecting retailers well beyond France. Third, regulatory fallout: a successful attack on food supply infrastructure is exactly the kind of incident that prompts new cybersecurity requirements for essential services. And fourth, whether the Ahold Delhaize "security issue" proves to be part of the same campaign — the answer will determine whether this was a French incident or a European one. What is established: hackers weaponized refrigeration systems across hundreds of French stores, food was destroyed and fires started, and a national investigation is now hunting the cause.